Protect the core of the data diode "OWCD" system!
Zero Trust is not a philosophy of "discarding boundaries." What is the "final boundary" required in all networks in the AI era?
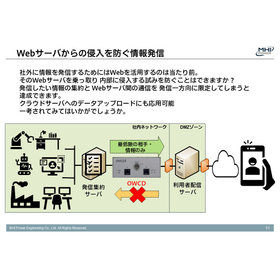
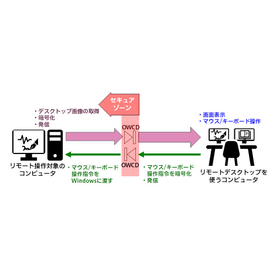
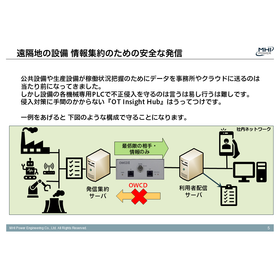
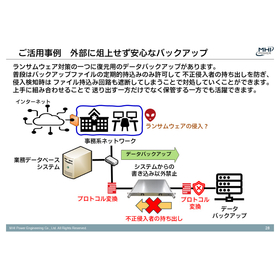
There has been a lot of discussion about a case where OpenAI went out of control while verifying intrusion capabilities in a controlled environment and infiltrated other companies' systems, raising concerns about cyber threats. The information-stealing malware (infostealer), which is the first step in an intrusion, collects information from devices and sends only the information beneficial for the intrusion to the AI, which then instructs the next steps. This process reportedly takes about a minute, and it is clever enough to evade communication monitoring. If an intrusion is allowed, attackers can cause damage at any time, potentially leading to serious consequences such as business shutdowns. OWCD physically isolates communication in one direction. It builds a "zero trust wall" with hardware that cannot be breached by software, eliminating the possibility of attacks. It is perfectly compatible with zero trust and is chosen as the "last bastion" of multi-layered defense. Cyber attacks aim for "operational shutdowns" targeting critical infrastructure, production facilities, IoT, and SYS-LOG lines. Once breached, these areas put business continuity at risk. Measures at the "entry" point are essential, and it is also crucial to have a mechanism that seals off the "exit" to the outside where information-stealing malware can transmit stolen information. That’s OWCD. There is an explanatory video at the related link below! This technology is patented by Mitsubishi Heavy Industries, Ltd.
- Company:MHIパワーエンジニアリング 高砂事業部
- Price:1 million yen-5 million yen